Vulnerability Description
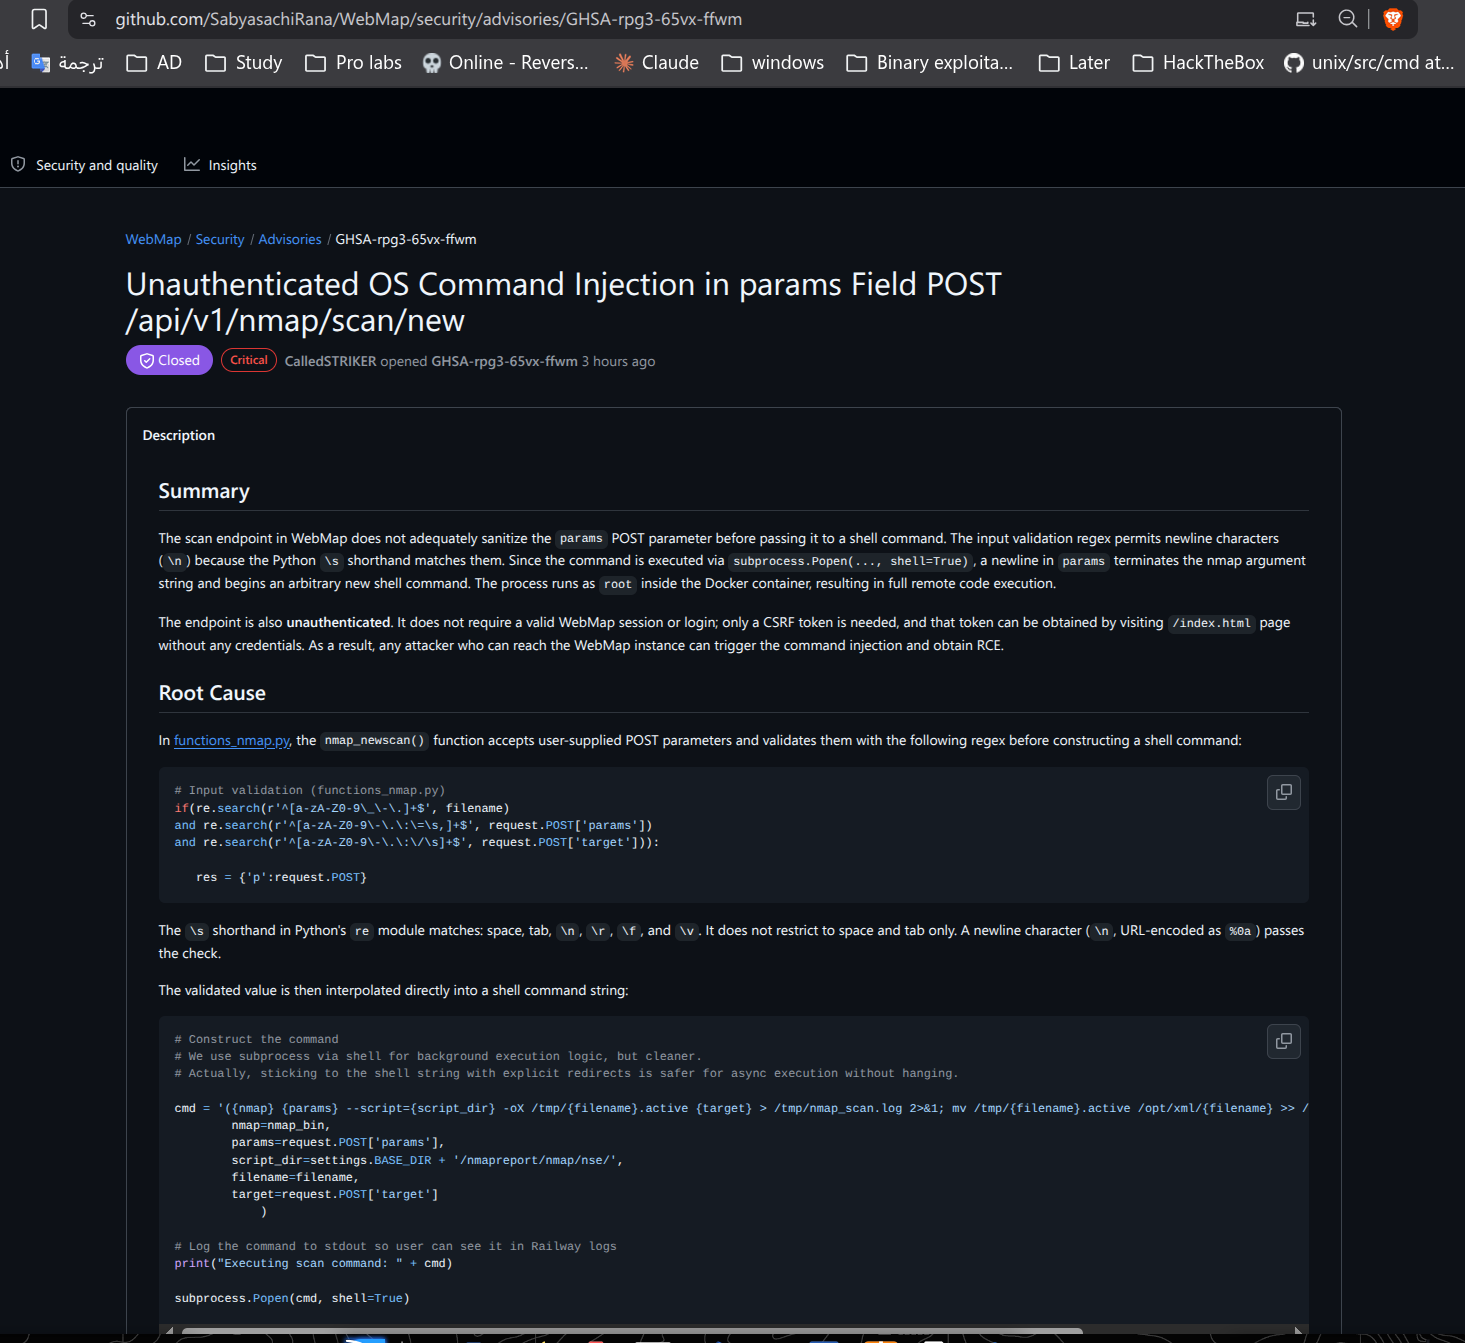
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
CVSS Score
HIGH
Related Weaknesses (CWE)
References
- https://calledstriker.gitbook.io/blog/security-research/webmap
- https://github.com/SabyasachiRana/WebMap/
- https://github.com/SabyasachiRana/WebMap/commit/3d52f65803a2716bff14d938352c6fef
- https://raw.githubusercontent.com/CalledSTRIKER/CalledSTRIKER-gitbook/refs/heads
- https://vuldb.com/cve/CVE-2026-90843
- https://vuldb.com/submit/925586
- https://vuldb.com/vuln/403395
- https://vuldb.com/vuln/403395/cti
FAQ
What is CVE-2026-90843?
CVE-2026-90843 is a vulnerability with a CVSS score of 8.3 (HIGH). A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the componen...
How severe is CVE-2026-90843?
CVE-2026-90843 has been rated HIGH with a CVSS base score of 8.3/10. Review the CVSS metrics above for detailed severity breakdown.
Is there a patch for CVE-2026-90843?
Check the references section above for vendor advisories and patch information. Review vendor security bulletins for remediation guidance.